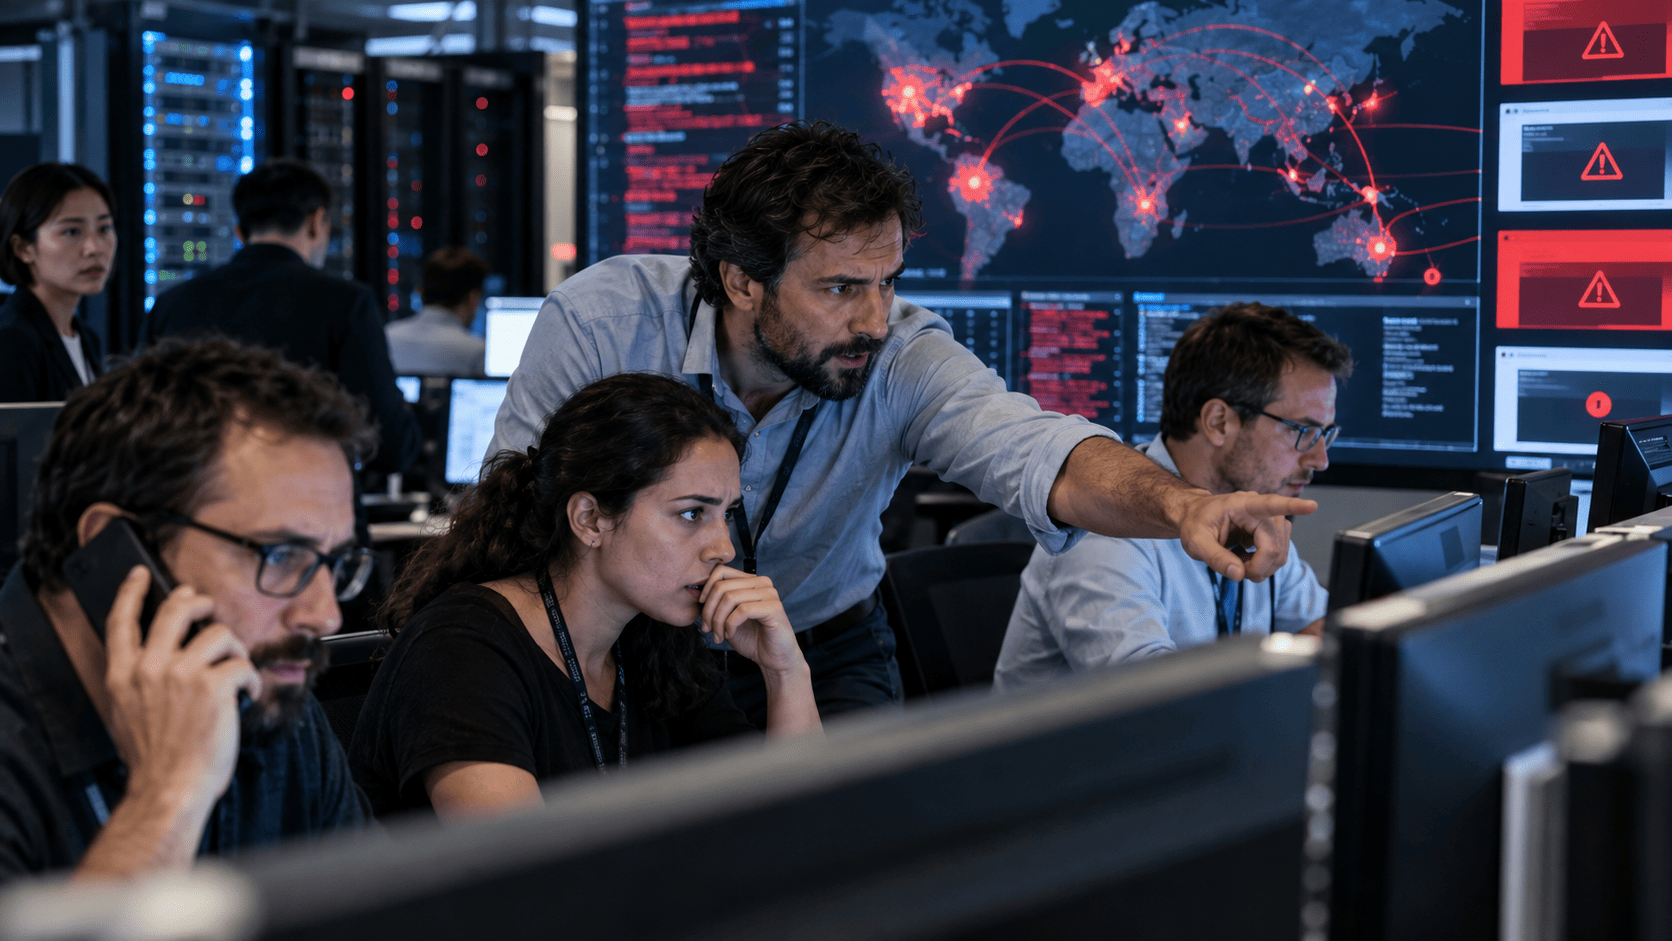
A pair of critical security flaws in PHP, the programming language that powers a large share of the internet, have triggered a global scramble to patch vulnerable systems. Government agencies and major corporations temporarily took websites offline as a precaution while developers rushed out emergency updates.
The vulnerabilities, tracked as CVE-2026-109618 and CVE-2026-109619, carry a severity score of 9.2 out of 10. They allow attackers to execute arbitrary code on servers without authentication, potentially compromising databases and sensitive customer data. The flaws stem from memory handling issues in PHP's processing of web requests.
Japan's Prime Minister Sanae Takaichi urged website operators to install the emergency security updates or consider temporarily suspending vulnerable services. Finland, the Netherlands, and France restricted some government websites, and the Wikimedia Foundation suspended certain systems. Mitsubishi UFJ, a major Japanese financial group, halted selected online services. These actions were precautionary; there was no immediate evidence that the affected organizations had been breached.
Security researchers used artificial intelligence tools to uncover the vulnerabilities, which had been present in PHP for over a decade. OpenAI reported that a researcher using its GPT-5.6 Sol model identified one of the flaws. Google's Wiz unit independently discovered both weaknesses using tools including Google's Gemini 4 Argon. The AI companies did not patch PHP themselves; the PHP maintainers led the engineering effort and released fixes on October 21, supported by researchers and infrastructure providers.
The involvement of AI highlights a double-edged sword. While it accelerates the discovery of dangerous bugs, it also gives attackers the ability to analyze newly published fixes before organizations have applied them. Raghu Nandakumara, an executive at cybersecurity firm Illumio, told the Associated Press that "speed without control creates a new kind of security problem."
Amazon's threat intelligence team detected a suspected exploitation attempt on October 17, four days before the public disclosure, using its MadPot decoy network. The activity came from an anonymized internet address, but Amazon could not determine how the attacker learned about the flaws. The company did not report any breaches among its customers. After disclosure, Cloudflare observed millions of exploitation attempts across its network, though none were confirmed successful intrusions.
PHP developers have released patched versions in branches 8.5.12, 8.4.27, 8.3.36, and 8.2.35. Older unsupported versions require upgrades or vendor-maintained fixes. Firewalls offer temporary protection but are not a substitute for patching.
The episode underscores how quickly an obscure software weakness can become a global problem. Alan Woodward, a cybersecurity professor at the University of Surrey, warned that poorly maintained sites could remain exposed for months after larger operators deploy fixes. "There is this race and some people unfortunately don't even know they are in the race," he told The Guardian.
As AI continues to reshape cybersecurity, the PHP incident serves as a reminder that the same tools that help defenders can also empower attackers. The race to patch is now on, and the outcome depends on how swiftly website operators act.
This article is for informational purposes only and does not constitute financial advice.